Regulation & Policy
GDPR
Also known as: General Data Protection Regulation
GDPR, the General Data Protection Regulation, is the European Union law that governs how organisations collect, store and use personal data about people in the EU. It came into force on 25 May 2018 and sets out lawful bases for processing, rights for individuals and obligations for controllers and processors. A parallel version, UK GDPR, applies in the United Kingdom alongside the Data Protection Act 2018.
What it is
GDPR is a data protection framework that applies to any organisation processing the personal data of people in the EU, regardless of where that organisation is based. It defines personal data broadly, covering identifiers such as names, email addresses, IP addresses and cookie identifiers. It also sets out roles, with the controller deciding why and how data is processed and the processor acting on the controller's instructions.
Why it matters
Almost every discovery and marketing activity touches personal data, from analytics and ad tracking to email capture and CRM enrichment. GDPR shapes what consent banners look like, which measurement data is available, and how much first party data a brand can legally build and use. Getting it wrong risks regulatory action, and can also degrade tracking coverage and audience quality if consent is handled badly.
How it works
Practitioners map what data is collected on each surface, record a lawful basis for each purpose, and implement consent management for cookies and similar technologies. Marketing teams work with legal and engineering colleagues on retention periods, data subject access requests, processor contracts and transfers outside the EU or UK. Consent state is then passed into analytics and ad platforms so measurement reflects what users have actually agreed to.
When it applies
It applies whenever you process personal data about people in the EU or UK, including website analytics, advertising, email marketing, lead forms and customer databases. It is most relevant when launching new tracking, adopting a new martech vendor or entering a European market.
Examples
- A SaaS company blocks analytics and advertising tags until a visitor gives consent through a consent management platform, then restores them based on the stored consent signal.
- A retailer documents legitimate interest for transactional email and consent for marketing newsletters, keeping separate records for each.
- A publisher signs a data processing agreement with an email platform and reviews where that platform stores and transfers subscriber data.
How it is measured
- Consent rate by surface and region, split into accept, reject and no interaction
- Proportion of sessions with analytics consent, used to gauge measurement coverage
- Time to fulfil data subject access and deletion requests
- Number of vendors with current data processing agreements and completed reviews
Related terms in Regulation & Policy
- AI complianceAI compliance is the work of making sure AI systems meet the laws, regulations, standards and internal policies that apply to them. It spans data protection, transparency, risk classification, documentation, human oversight and record keeping across the life of a system. In practice it combines legal interpretation, engineering controls and ongoing evidence gathering.
- AI governanceAI governance is the set of policies, roles, controls and review processes an organisation uses to manage how AI systems are built, bought and used. It covers risk assessment, documentation, human oversight, data handling and accountability. It applies both to AI a company develops and to third-party AI tools used by staff.
- AI privacyAI privacy is the set of practices, rights and obligations that govern how personal data is collected, used, stored and exposed when building or using AI systems. It covers training data, prompts and outputs, retention by AI vendors, and the transparency and control offered to the people whose data is involved. For marketing teams it shapes what customer data can safely be put into AI tools and what must be disclosed.
- AI safetyAI safety is the practice of designing, testing and operating AI systems so they cause less harm, behave predictably and resist misuse. It covers alignment with intended behaviour, evaluation and red teaming, content guardrails, and monitoring once a system is live. For marketers it shapes what models will say, how assistants handle brands, and what compliance teams expect before AI tools go into production.
- AI transparencyAI transparency is the practice of making clear how an AI system works, what sits behind it, and when content or an interaction involves AI. It covers regulatory disclosure duties as well as voluntary explanations such as model cards, labels on synthetic media and citations in AI generated answers. For publishers and marketers it sets expectations about when AI involvement should be declared and how clearly.
- Competition and Markets AuthorityThe Competition and Markets Authority (CMA) is the United Kingdom's competition and consumer protection regulator. It investigates mergers, anti-competitive conduct and market practices, and it holds specific powers over large digital firms under the Digital Markets, Competition and Consumers Act 2024. Its decisions shape how search engines, app stores and AI assistants operate in the UK market.
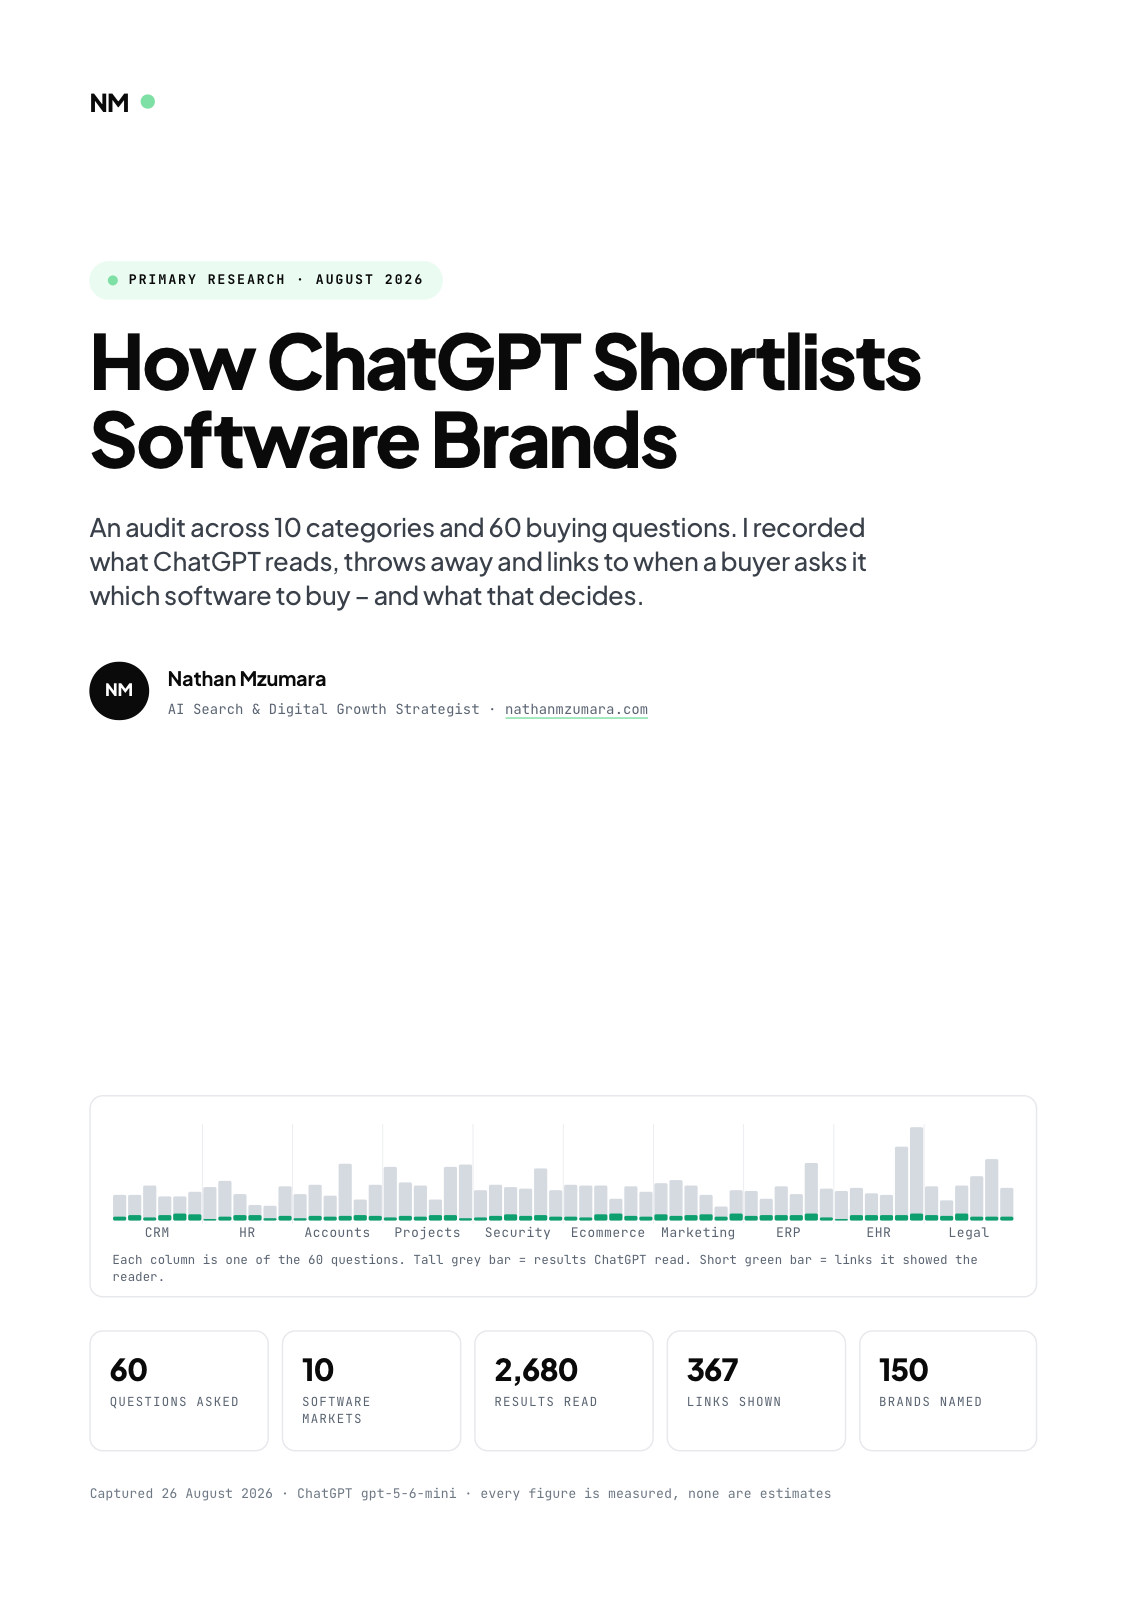
Primary research · August 2026
How ChatGPT Shortlists Software Brands
An audit across 10 categories and 60 buying questions. I recorded what ChatGPT reads, throws away and links to when a buyer asks it which software to buy, and what that decides.
- 60
- Questions asked
- 10
- Software markets
- 2,680
- Results read
- 367
- Links shown
Free download
Get the full report
35 pages · PDF · 536 KB. Enter your details and it downloads straight away.