Regulation & Policy
AI compliance
Also known as: AI regulatory compliance
AI compliance is the work of making sure AI systems meet the laws, regulations, standards and internal policies that apply to them. It spans data protection, transparency, risk classification, documentation, human oversight and record keeping across the life of a system. In practice it combines legal interpretation, engineering controls and ongoing evidence gathering.
What it is
AI compliance covers obligations from instruments such as the EU AI Act, data protection law including the UK GDPR, sector rules in finance or health, and voluntary standards like ISO/IEC 42001 and the NIST AI Risk Management Framework. It applies to systems you build and to third party models and tools you deploy. The output is usually an inventory, a risk classification for each use case, and documented controls with evidence.
Why it matters
Non compliance can stall launches, trigger legal exposure and lose enterprise deals where buyers demand assurance before signing. For marketing and discovery work it also touches disclosure of AI generated content, consent for personal data used in personalisation, and honesty in claims about automated systems. Getting this right early is far cheaper than retrofitting controls after a product is live.
How it works
Teams start with an inventory of AI use cases, classify each by risk and applicable rules, then assign owners and controls such as data minimisation, human review, logging, evaluation and incident handling. Documentation is maintained as a living record, including data sources, model versions, testing results and decisions, so it can be produced for auditors or customers. Reviews are repeated when models, vendors or use cases change, because compliance status is not static.
When it applies
It applies from the moment an AI use case is proposed, and especially when it touches personal data, decisions about individuals, regulated sectors, or markets with specific AI legislation.
Examples
- A marketing team documents lawful basis and consent for using customer data in an AI personalisation model.
- A bank classifies an AI credit support tool as higher risk and adds mandatory human review plus decision logging.
- A SaaS vendor completes an AI questionnaire and supplies model documentation as part of an enterprise security review.
How it is measured
- Share of AI use cases inventoried and risk classified
- Percentage of systems with complete, current documentation and named owners
- Median time to close compliance findings or remediation actions
- Number of failed customer assurance reviews or regulatory queries per period
Related terms in Regulation & Policy
- AI governanceAI governance is the set of policies, roles, controls and review processes an organisation uses to manage how AI systems are built, bought and used. It covers risk assessment, documentation, human oversight, data handling and accountability. It applies both to AI a company develops and to third-party AI tools used by staff.
- AI privacyAI privacy is the set of practices, rights and obligations that govern how personal data is collected, used, stored and exposed when building or using AI systems. It covers training data, prompts and outputs, retention by AI vendors, and the transparency and control offered to the people whose data is involved. For marketing teams it shapes what customer data can safely be put into AI tools and what must be disclosed.
- AI safetyAI safety is the practice of designing, testing and operating AI systems so they cause less harm, behave predictably and resist misuse. It covers alignment with intended behaviour, evaluation and red teaming, content guardrails, and monitoring once a system is live. For marketers it shapes what models will say, how assistants handle brands, and what compliance teams expect before AI tools go into production.
- AI transparencyAI transparency is the practice of making clear how an AI system works, what sits behind it, and when content or an interaction involves AI. It covers regulatory disclosure duties as well as voluntary explanations such as model cards, labels on synthetic media and citations in AI generated answers. For publishers and marketers it sets expectations about when AI involvement should be declared and how clearly.
- Competition and Markets AuthorityThe Competition and Markets Authority (CMA) is the United Kingdom's competition and consumer protection regulator. It investigates mergers, anti-competitive conduct and market practices, and it holds specific powers over large digital firms under the Digital Markets, Competition and Consumers Act 2024. Its decisions shape how search engines, app stores and AI assistants operate in the UK market.
- Content licensingContent licensing is the practice of granting an AI company or platform permission to use your published material, usually for model training, retrieval or display inside an assistant, in return for payment or other terms. Deals set out what content is covered, how it can be used, how it is attributed and for how long. It is the commercial alternative to relying only on crawler blocking or copyright enforcement.
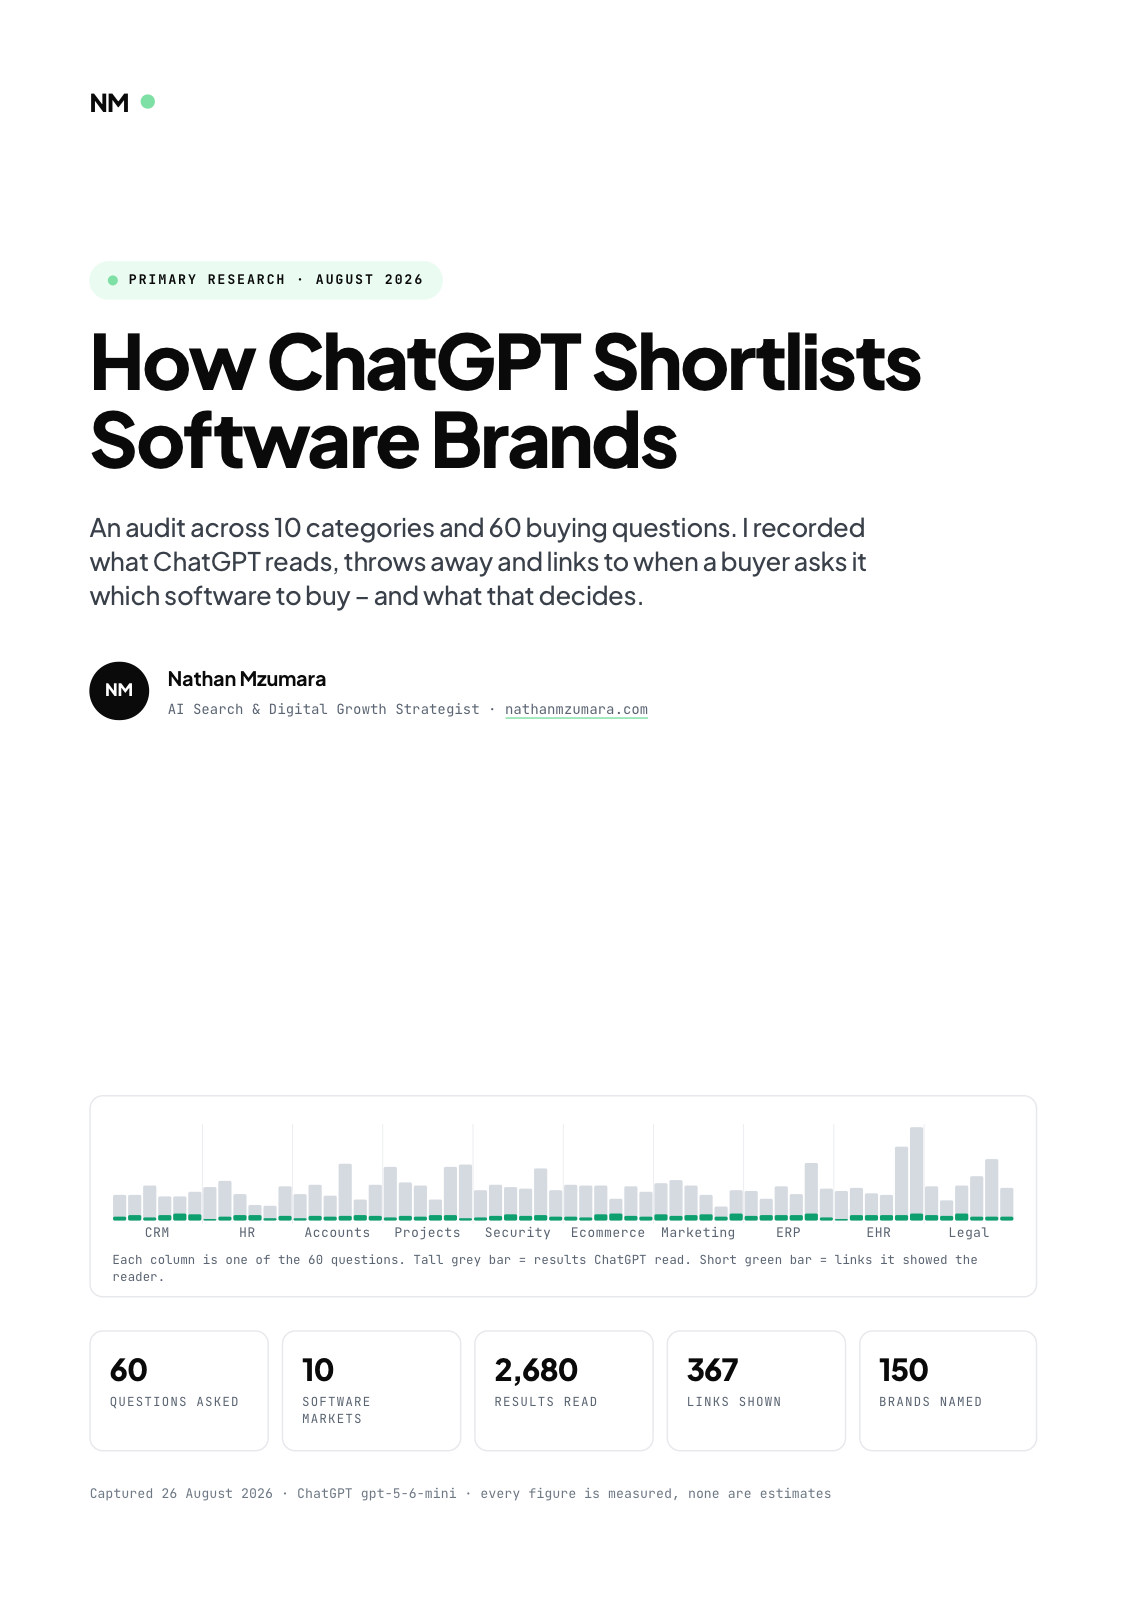
Primary research · August 2026
How ChatGPT Shortlists Software Brands
An audit across 10 categories and 60 buying questions. I recorded what ChatGPT reads, throws away and links to when a buyer asks it which software to buy, and what that decides.
- 60
- Questions asked
- 10
- Software markets
- 2,680
- Results read
- 367
- Links shown
Free download
Get the full report
35 pages · PDF · 536 KB. Enter your details and it downloads straight away.