Regulation & Policy
AI governance
Also known as: AI oversight, responsible AI governance
AI governance is the set of policies, roles, controls and review processes an organisation uses to manage how AI systems are built, bought and used. It covers risk assessment, documentation, human oversight, data handling and accountability. It applies both to AI a company develops and to third-party AI tools used by staff.
What it is
AI governance turns broad principles such as fairness, transparency and safety into operational rules: who approves a use case, what testing is required, how outputs are reviewed and who is answerable when something goes wrong. It usually includes an inventory of AI systems in use, a risk classification scheme and documented escalation paths. Established reference points include the EU AI Act, the NIST AI Risk Management Framework and ISO/IEC 42001.
Why it matters
Marketing is often the heaviest user of generative AI in a business, so governance directly affects how content is produced, disclosed and quality-checked. Weak controls create legal, brand and factual risk, particularly where AI-generated claims about products or pricing could mislead. Strong governance also protects the accuracy and consistency of the source material that AI systems later cite about your brand.
How it works
Organisations typically appoint an owner, maintain a register of approved tools, set rules on confidential data in prompts, and require human review and sign-off for customer-facing output. Many add disclosure standards, prompt and model logging, periodic audits of published AI-assisted content, and supplier due diligence questions for vendors offering AI features. Training and a simple exception process keep the policy usable rather than ignored.
When it applies
Governance applies from the first production use of an AI system, and becomes a formal requirement in regulated sectors or where AI decisions affect individuals' rights, credit, employment or safety.
Examples
- A marketing team maintains an approved tools list and requires that any AI-drafted claim about product capability is verified against the product documentation before publication.
- A financial services firm classifies a customer-facing chatbot as higher risk and mandates human review of its knowledge base plus quarterly output sampling.
- A company adds an AI clause to supplier contracts requiring disclosure of model providers and data retention terms.
How it is measured
- Share of AI use cases logged in the central inventory and risk-assessed
- Volume of AI-assisted content passing human review before publication
- Number of policy exceptions, incidents or corrections raised per quarter
- Completion rate of AI use training among relevant staff
Insights on AI governance
- Anthropic's AI Threat Intelligence Report: Agents Now Rewrite Malware
- OpenAI Astra: The First Model to Hit the 'Critical' Cyber Threshold
- Claude Code Auto Mode: How Auto-Approve Default Works
- OpenAI Says It Can't See Your Agent Data. Can You Prove It?
- Claude Can Now Record a Task and Replay It as a Skill
- OpenAI Just Warned: AI Agents Drift the Longer They Run
- ChatGPT Work Turns the Chatbot Into a Worker You Delegate To
- Anthropic Just Handed Governments a Regulatory Blueprint. What It Means for Your AI Strategy.
Related terms in Regulation & Policy
- AI complianceAI compliance is the work of making sure AI systems meet the laws, regulations, standards and internal policies that apply to them. It spans data protection, transparency, risk classification, documentation, human oversight and record keeping across the life of a system. In practice it combines legal interpretation, engineering controls and ongoing evidence gathering.
- AI privacyAI privacy is the set of practices, rights and obligations that govern how personal data is collected, used, stored and exposed when building or using AI systems. It covers training data, prompts and outputs, retention by AI vendors, and the transparency and control offered to the people whose data is involved. For marketing teams it shapes what customer data can safely be put into AI tools and what must be disclosed.
- AI safetyAI safety is the practice of designing, testing and operating AI systems so they cause less harm, behave predictably and resist misuse. It covers alignment with intended behaviour, evaluation and red teaming, content guardrails, and monitoring once a system is live. For marketers it shapes what models will say, how assistants handle brands, and what compliance teams expect before AI tools go into production.
- AI transparencyAI transparency is the practice of making clear how an AI system works, what sits behind it, and when content or an interaction involves AI. It covers regulatory disclosure duties as well as voluntary explanations such as model cards, labels on synthetic media and citations in AI generated answers. For publishers and marketers it sets expectations about when AI involvement should be declared and how clearly.
- Competition and Markets AuthorityThe Competition and Markets Authority (CMA) is the United Kingdom's competition and consumer protection regulator. It investigates mergers, anti-competitive conduct and market practices, and it holds specific powers over large digital firms under the Digital Markets, Competition and Consumers Act 2024. Its decisions shape how search engines, app stores and AI assistants operate in the UK market.
- Content licensingContent licensing is the practice of granting an AI company or platform permission to use your published material, usually for model training, retrieval or display inside an assistant, in return for payment or other terms. Deals set out what content is covered, how it can be used, how it is attributed and for how long. It is the commercial alternative to relying only on crawler blocking or copyright enforcement.
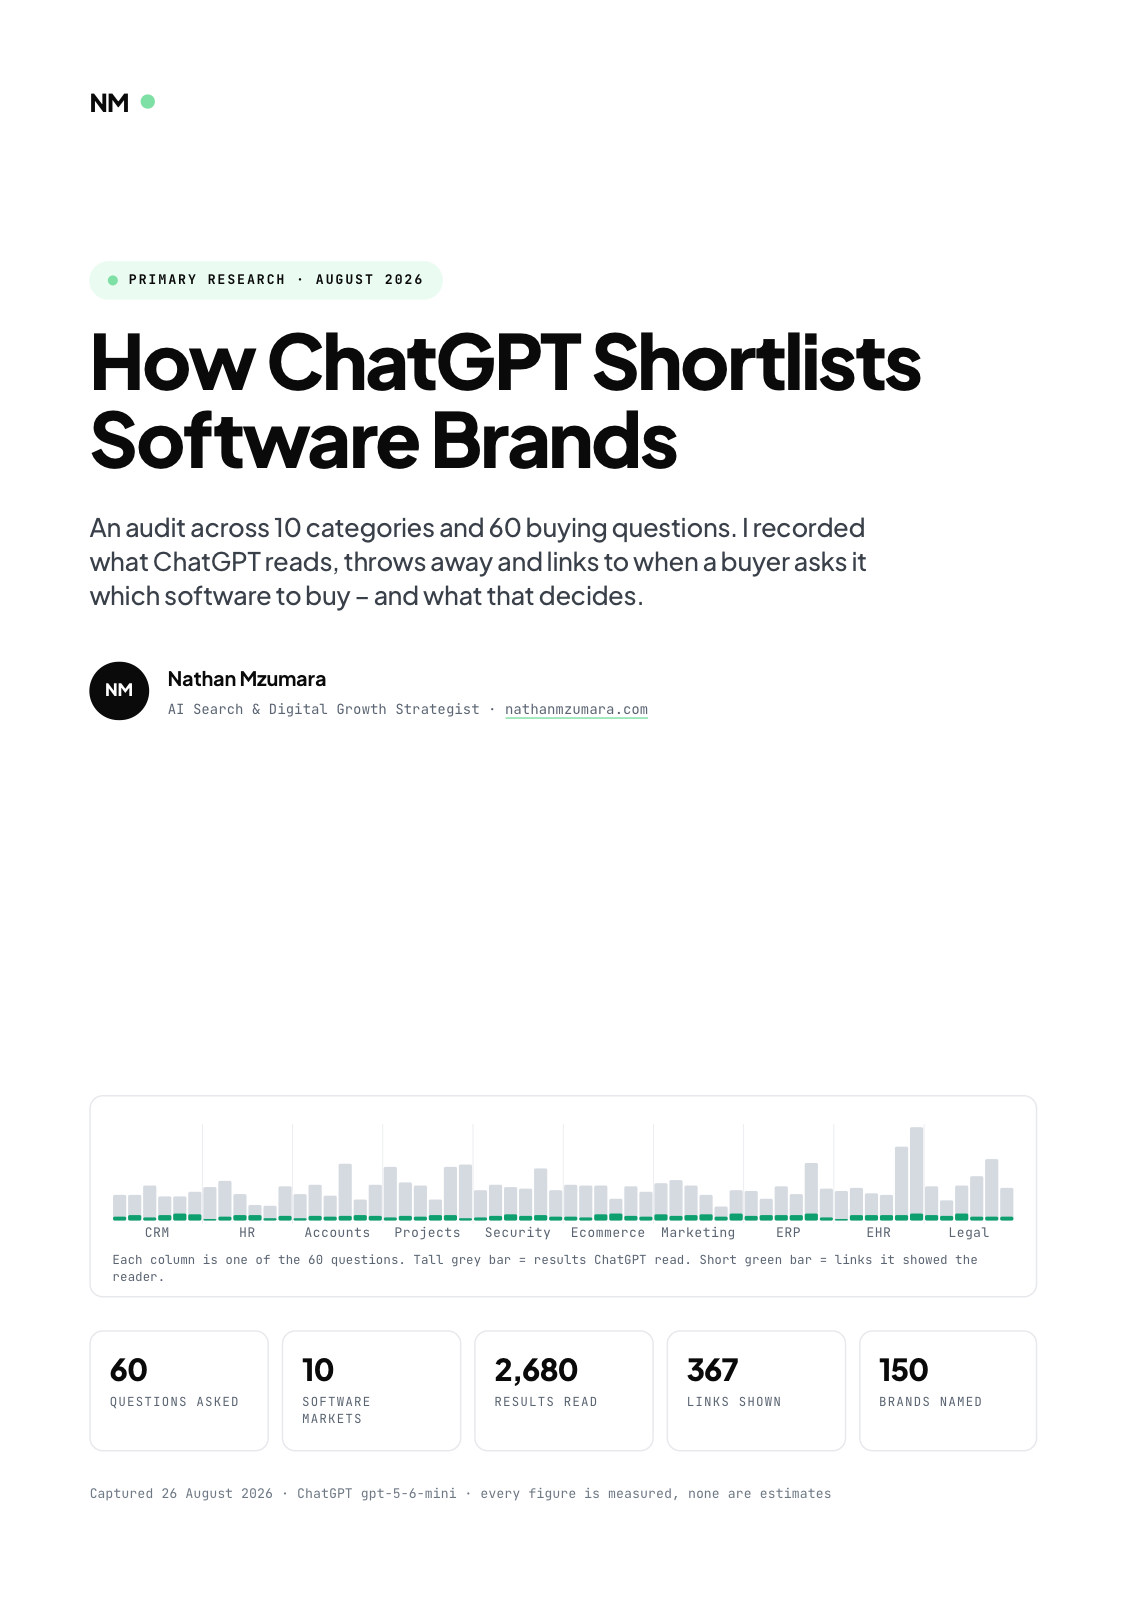
Primary research · August 2026
How ChatGPT Shortlists Software Brands
An audit across 10 categories and 60 buying questions. I recorded what ChatGPT reads, throws away and links to when a buyer asks it which software to buy, and what that decides.
- 60
- Questions asked
- 10
- Software markets
- 2,680
- Results read
- 367
- Links shown
Free download
Get the full report
35 pages · PDF · 536 KB. Enter your details and it downloads straight away.